The Hidden Threat: What Is a Zero Day Exploit and Why It Matters
Cybersecurity isn’t just about firewalls and antivirus software—it’s a high-stakes game of cat and mouse between defenders and attackers. At the heart of this conflict lies a term that sends chills down the spines of IT professionals: what is a zero day exploit. Unlike conventional vulnerabilities that get patched after discovery, a zero day exploit targets flaws in software, hardware, or systems that are unknown to developers and users. The "zero day" refers to the fact that vendors have had zero days to prepare a fix, leaving millions of devices exposed until an update is released—or worse, never.
These exploits don’t announce themselves. They lurk in the shadows, exploited by nation-states, cybercriminal syndicates, and even lone hackers with advanced skills. The damage? Ransomware that cripples hospitals, espionage that steals military secrets, or financial fraud that drains accounts before anyone notices. The stakes couldn’t be higher: in 2023 alone, zero day vulnerabilities accounted for 60% of critical breaches tracked by major cybersecurity firms. Yet most people—even those in tech—struggle to grasp the full scope of what makes them so devastating.
The problem isn’t just technical. It’s psychological. A zero day exploit thrives on the element of surprise, exploiting the human tendency to assume "if it’s not broken, it’s safe." But in the digital age, safety isn’t binary—it’s a spectrum of unknown risks. Understanding what is a zero day exploit isn’t just about protecting data; it’s about recognizing that the next attack could be silent, invisible, and already underway.

The Complete Overview of What Is a Zero Day Exploit
A zero day exploit is a cyberattack that leverages an unknown vulnerability in software, hardware, or a system configuration. The term "zero day" originates from the fact that developers have zero days to release a patch before the exploit is weaponized. Unlike traditional vulnerabilities—where researchers disclose flaws and vendors rush fixes—zero day exploits operate in the dark, often sold on underground markets or used by attackers before anyone outside a closed group knows they exist.The danger lies in their stealth. Attackers don’t need to break into a system; they exploit a flaw that was never intended to be exposed. This could be a misconfigured server, a poorly written API, or a deep flaw in an operating system’s core architecture. The most notorious examples—like EternalBlue (used in the WannaCry ransomware attack) or Log4Shell—demonstrate how a single zero day can trigger global chaos. Governments and corporations spend billions to mitigate these threats, yet the cat-and-mouse game continues, with new exploits emerging faster than defenses can adapt.
Historical Background and Evolution
The concept of zero day exploits predates the digital era but took on modern form with the rise of commercial software in the 1980s. Early hackers exploited bugs in operating systems like DOS, but the term "zero day" gained traction in the 1990s as underground hacking communities began trading unpatched vulnerabilities. The first recorded zero day attack targeted Internet Explorer in 1999, a flaw that allowed remote code execution—a technique still used today.The 2000s saw zero day exploits become a geopolitical weapon. Stuxnet, a joint U.S.-Israeli operation, used four zero day vulnerabilities to sabotage Iran’s nuclear program in 2010. This marked a turning point: zero day exploits were no longer just tools for criminals but instruments of state-sponsored cyberwarfare. By 2017, the WannaCry ransomware—which spread via the EternalBlue exploit—infected over 200,000 systems in 150 countries, causing an estimated $4 billion in damages. These incidents proved that what is a zero day exploit isn’t just a technical question—it’s a strategic one.
Table of Contents
- The Complete Overview of What Is a Zero Day Exploit
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: Can a zero day exploit be stopped?
- Q: How do hackers find zero day vulnerabilities?
- Q: Are zero day exploits legal?
- Q: How long does a zero day exploit typically remain active?
- Q: What’s the most famous zero day exploit in history?
- Q: Can individuals protect themselves from zero day attacks?
- Q: Why do governments hoard zero day exploits?
Today, the zero day market is a shadow economy worth hundreds of millions annually. Exploits are traded on dark web forums, with prices ranging from $50,000 for a basic flaw to $1 million for a zero day in widely used enterprise software. Nation-states hoard exploits for espionage, while cybercriminals rent them for targeted attacks. The evolution of zero day exploits reflects a darker truth: the digital world’s security infrastructure is perpetually playing catch-up.
Core Mechanisms: How It Works
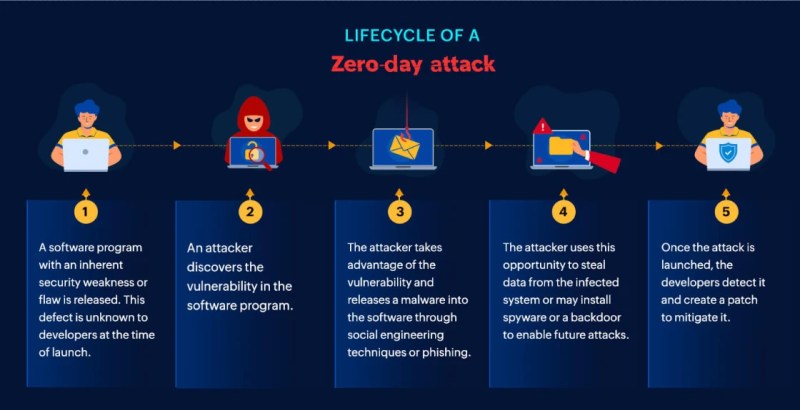
At its core, a zero day exploit follows a predictable—but devastating—flow. First, an attacker discovers or acquires a vulnerability that hasn’t been documented or patched. This could come from reverse engineering (studying compiled code), fuzzing (feeding random inputs to crash software), or social engineering (tricking developers into revealing flaws). Once the vulnerability is identified, the attacker crafts an exploit—a piece of code or sequence of actions that triggers the flaw to execute malicious payloads.The exploit’s effectiveness depends on three factors:
1. Stealth – The attack must avoid detection by antivirus, firewalls, or intrusion detection systems.
2. Persistence – The vulnerability must remain unpatched long enough for the attacker to achieve their goal (data theft, ransomware deployment, etc.).
3. Scalability – Some zero days, like EternalBlue, spread automatically across networks, amplifying damage exponentially.
The most dangerous zero days exploit memory corruption vulnerabilities (e.g., buffer overflows) or logic flaws in authentication systems. For example, the Log4Shell vulnerability in 2021 allowed attackers to remotely execute code by manipulating log messages—a flaw so severe that the U.S. Cybersecurity and Infrastructure Security Agency (CISA) called it an "existential threat" to the internet.
Key Benefits and Crucial Impact
Zero day exploits aren’t just a technical curiosity—they represent a fundamental shift in how cyber threats operate. For attackers, they offer unprecedented power: no need to brute-force passwords or rely on phishing when you can bypass security entirely. Governments and cybercriminals prioritize zero days because they provide asymmetric advantage—a single exploit can neutralize an entire organization’s defenses overnight. The impact isn’t just financial; it’s existential for critical infrastructure, where a zero day could mean life-or-death consequences.Yet the term "what is a zero day exploit" is often misunderstood. Many assume it’s a single, dramatic attack, but in reality, zero days are silent enablers—the invisible force behind ransomware, data breaches, and state-sponsored espionage. The 2023 LockBit ransomware attacks, which crippled hospitals and governments, relied heavily on zero day exploits to evade detection. Similarly, the 2020 SolarWinds breach, one of the most sophisticated cyberespionage campaigns in history, used a zero day to infiltrate Microsoft’s update mechanism.
"A zero day exploit is the cyber equivalent of a nuclear option—it doesn’t just break systems; it redefines the rules of engagement." — Mikko Hypponen, Chief Research Officer at F-Secure
Major Advantages
For attackers, zero day exploits offer five critical advantages:For defenders, the challenge is equally daunting: what is a zero day exploit forces a shift from reactive to predictive security, where organizations must assume they’re already compromised and focus on detection and containment.
Comparative Analysis
Not all exploits are zero days. Understanding the differences is key to grasping their unique threat level.| Zero Day Exploit | Known Vulnerability Exploit |
|---|---|
|
|
| Detection Evasion | Detection Likelihood |
|
|
| Mitigation Strategy | Mitigation Strategy |
|
|
Future Trends and Innovations
The arms race between zero day exploits and cybersecurity defenses is accelerating. One emerging trend is AI-driven exploitation, where machine learning models automatically discover and weaponize vulnerabilities at scale. Tools like DeepExploit demonstrate how AI can generate zero day attacks by analyzing software behavior patterns—raising the stakes for defenders who must now contend with automated, adaptive threats.Another shift is the commercialization of zero days. Companies like Kaspersky and CrowdStrike now offer "bug bounty" programs to responsibly disclose vulnerabilities, but the underground market remains robust. Meanwhile, quantum computing could revolutionize zero day attacks by breaking encryption algorithms that protect software integrity, making exploits even harder to detect.
The future of what is a zero day exploit will likely hinge on proactive security models. Traditional perimeter defenses are obsolete; the next frontier is predictive threat intelligence, where AI analyzes attack patterns to anticipate zero days before they’re exploited. However, the cat-and-mouse game will persist—because as long as software exists, there will be flaws, and as long as there are flaws, there will be those who exploit them.

Conclusion
Zero day exploits are the silent architects of modern cyber warfare. They don’t announce themselves with fanfare; they strike when least expected, leaving organizations scrambling to respond. Understanding what is a zero day exploit isn’t just about technical knowledge—it’s about recognizing that security isn’t a product but a continuous, adaptive process.The lessons are clear: assume breach, invest in zero trust architectures, and prioritize threat intelligence. The next zero day could be lurking in an unpatched server, a third-party vendor, or even a seemingly harmless software update. The question isn’t if it will happen—but when. And when it does, the organizations prepared to detect, contain, and recover will be the ones that survive.
Comprehensive FAQs
Q: Can a zero day exploit be stopped?
A: Not entirely. Since zero days target unknown vulnerabilities, traditional defenses like firewalls and antivirus are ineffective. However, organizations can reduce risk through Zero Trust security models, runtime application protection, and continuous vulnerability scanning. The goal isn’t elimination but minimizing exposure until a patch is available.
Q: How do hackers find zero day vulnerabilities?
A: Attackers use several methods, including:
- Reverse engineering – Analyzing compiled software to find flaws.
- Fuzzing – Feeding random inputs to crash or exploit software.
- Supply chain attacks – Compromising developers or vendors to insert flaws.
- Insider threats – Employees or contractors with access to source code.
- AI-assisted discovery – Using machine learning to identify patterns in code.
Q: Are zero day exploits legal?
A: Legality depends on intent and context. Discovering a zero day is not illegal, but exploiting it without permission is. Many countries have laws against unauthorized hacking (e.g., the Computer Fraud and Abuse Act in the U.S.). However, ethical hackers and governments sometimes use zero days for defensive purposes (e.g., cybersecurity research or national security). The ethical debate centers on responsible disclosure—whether to inform vendors immediately or wait for a strategic advantage.
Q: How long does a zero day exploit typically remain active?
A: The lifespan varies. Some zero days are exploited within days (e.g., in ransomware attacks), while others remain hidden for months or years (e.g., state-sponsored espionage). The average time between discovery and patch is 30-90 days, but high-value exploits (like those used in cyberwarfare) may never be patched if the attacker maintains control. The longer a zero day remains active, the greater the potential damage.
Q: What’s the most famous zero day exploit in history?
A: Two stand out:
- EternalBlue (2017) – A Windows SMB vulnerability exploited by WannaCry, causing $4 billion in damages across 150 countries. It was originally developed by the NSA and leaked by the Shadow Brokers hacking group.
- Log4Shell (2021) – A critical flaw in the Log4j logging library, affecting billions of devices. It allowed remote code execution with minimal effort, earning a 10/10 severity score from the CVSS vulnerability scoring system.
Q: Can individuals protect themselves from zero day attacks?
A: While individuals can’t stop zero days entirely, they can reduce risk with these steps:
- Keep software updated – Even if a zero day is unknown, patches for related flaws may help.
- Avoid pirated or cracked software – Many zero days originate from unpatched or modified versions.
- Use multi-factor authentication (MFA) – Even if credentials are stolen, MFA adds a critical layer.
- Monitor for unusual activity – Behavioral analysis tools can detect anomalies before damage spreads.
- Limit exposure – Avoid clicking suspicious links, opening unknown files, or using public Wi-Fi for sensitive transactions.
Q: Why do governments hoard zero day exploits?
A: Governments hoard zero days primarily for espionage and offensive cyber operations. The logic is simple:
- Strategic advantage – A zero day can be used to spy on adversaries without detection.
- Denial of defense – By keeping exploits secret, governments prevent enemies from patching vulnerabilities.
- Plausible deniability – Attacks using zero days are harder to attribute.
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of Viralcontentbee.