How to Enable Secure Boot Windows 10: A Definitive Security Guide
Windows 10’s Secure Boot feature stands as a critical defense mechanism against firmware-level attacks, yet many users remain unaware of its existence or how to activate it. Without enabling how to enable Secure Boot Windows 10, systems remain vulnerable to exploits targeting the boot process—where malware can embed itself before Windows even loads. The feature, when properly configured, verifies the digital signatures of all boot components, ensuring only trusted code executes during startup. This isn’t just theoretical; real-world attacks like bootkits (e.g., LoJax) have demonstrated how disabling Secure Boot can turn a standard PC into a compromised platform within minutes.
The process of enabling Secure Boot in Windows 10 isn’t just about flipping a switch in the BIOS—it requires careful consideration of hardware compatibility, existing drivers, and potential third-party software conflicts. Legacy systems with outdated firmware or unsigned components may fail to boot entirely after activation, leaving users scrambling for recovery options. Yet, the trade-offs are clear: the security benefits far outweigh the risks for most modern setups, provided the steps are followed precisely. This guide cuts through the ambiguity, offering a structured approach to activation while addressing common pitfalls.
For enterprise environments or high-security workstations, how to enable Secure Boot Windows 10 becomes non-negotiable. Microsoft’s push for UEFI-based systems (and the phasing out of Legacy BIOS) has made Secure Boot a standard expectation, yet many IT administrators still treat it as optional. The reality is that without it, even a fully patched Windows 10 system remains exposed to boot-time malware, rootkits, and supply-chain attacks targeting the firmware. The following breakdown ensures you understand not just how to enable it, but why it matters—and how to troubleshoot when things go wrong.

The Complete Overview of How to Enable Secure Boot Windows 10
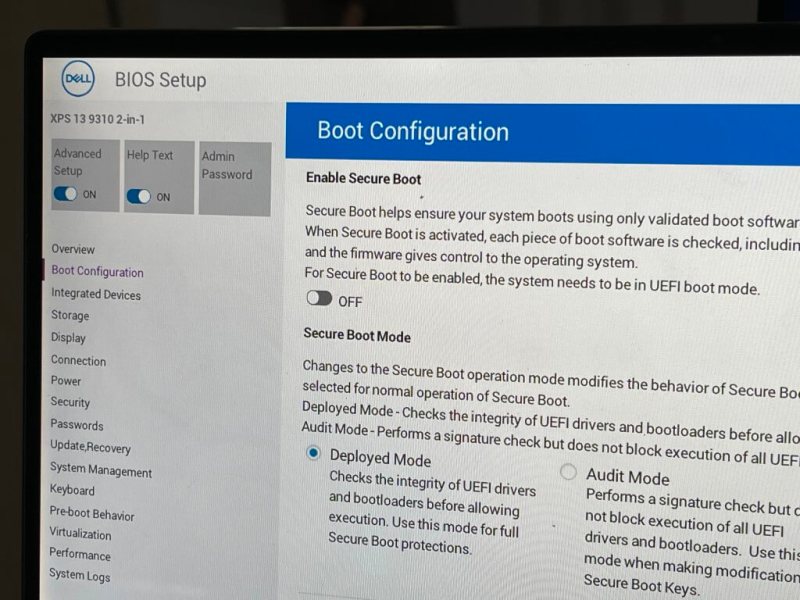
Enabling Secure Boot in Windows 10 is a two-phase process: first, verifying system compatibility with UEFI firmware and signed components, and second, configuring the BIOS/UEFI settings to enforce signature checks. The modern Windows 10 installation already includes Secure Boot by default in most cases, but legacy systems or custom configurations may require manual intervention. The key lies in understanding whether your system uses UEFI mode (a prerequisite) and whether third-party bootloaders (like GRUB or older Linux installers) are present, which may need temporary exemptions.The activation process itself is straightforward but varies slightly depending on whether you’re using a pre-built OEM system (e.g., Dell, HP) or a custom-built PC. OEMs often pre-configure Secure Boot in their BIOS, but it may be disabled by default to ensure compatibility with older operating systems. For custom builds, the steps are identical, though you’ll need to ensure your motherboard’s firmware supports UEFI 2.3.1 or later—a standard since 2011. The critical step is accessing the UEFI setup utility (not the legacy BIOS), where Secure Boot resides under the Security or Boot tab. From there, enabling it triggers Windows to verify all boot files against Microsoft’s Secure Boot database (DB) during each startup.
Historical Background and Evolution
Secure Boot’s origins trace back to the UEFI forum’s 2007 specification, designed as a response to the growing threat of boot-sector viruses and rootkits that operated below the operating system level. Before UEFI, BIOS systems relied on simple checksums or no verification at all, allowing malware like CIH or Stoned Boot to persist across reboots. Microsoft’s adoption of Secure Boot in Windows 8 (2012) marked a turning point, forcing OEMs to ship systems with the feature enabled by default. However, the transition wasn’t seamless—many users and IT departments resisted due to compatibility issues with unsigned Linux kernels, custom bootloaders, or legacy hardware.The evolution of how to enable Secure Boot Windows 10 reflects broader shifts in computing security. With the rise of firmware-based attacks (e.g., BadUSB, Thunderspy), Microsoft and UEFI forum expanded the feature to include dynamic root of trust for measuring (DRTM) and secure boot for measured boot (SBMB). Today, Secure Boot is a cornerstone of Windows 10’s security baseline, integrated with BitLocker, Windows Defender, and Device Guard to create a layered defense. Yet, its effectiveness hinges on proper configuration—a gap that persists in both consumer and enterprise deployments.
Core Mechanisms: How It Works
At its core, Secure Boot operates on a trust chain that begins with the UEFI firmware itself. When enabled, the system checks the signature of the bootloader (e.g., `winload.efi`) against a public key database stored in the UEFI variables. If the signature is valid, the bootloader is executed; if not, the system halts with an error (e.g., "Secure Boot violation"). This chain extends to kernel modules, drivers, and even third-party boot managers, ensuring no unsigned code runs during startup.Table of Contents
- The Complete Overview of How to Enable Secure Boot Windows 10
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: Can I enable Secure Boot on a Windows 10 system with Legacy BIOS?
- Q: Will enabling Secure Boot break my dual-boot setup with Linux?
- Q: What should I do if Windows 10 fails to boot after enabling Secure Boot?
- Q: Does Secure Boot prevent all types of malware?
- Q: How do I check if Secure Boot is already enabled on my Windows 10 system?
- Q: Can I enable Secure Boot on Windows 10 Home edition?
- Q: What’s the difference between Secure Boot and BitLocker?
- Q: Will enabling Secure Boot void my warranty?
- Q: How often should I update my Secure Boot keys?
- Q: Can I disable Secure Boot later if needed?
The process relies on three key components:
1. Secure Boot Keys: Microsoft’s Platform Key (PK), Key Exchange Key (KEK), and Signature Database (DB) are embedded in the UEFI firmware. These keys are used to verify the authenticity of boot components.
2. UEFI Variables: Stored in non-volatile memory (NVRAM), these variables define which keys are trusted and whether Secure Boot is enforced.
3. Signature Verification: Each boot file must be signed by a trusted certificate authority (CA). Windows 10 includes Microsoft’s CA by default, but administrators can add their own keys via `bcdedit` or UEFI tools.
The mechanism isn’t foolproof—shim loaders (used by Linux distributions) and custom boot environments can bypass checks—but when configured correctly, it raises the bar for attackers targeting the boot process.
Key Benefits and Crucial Impact
The decision to enable Secure Boot in Windows 10 isn’t just about ticking a security checkbox—it’s about mitigating risks that traditional antivirus solutions can’t address. Malware like bootkits (which infect the Master Boot Record or UEFI firmware) can persist across OS reinstalls, but Secure Boot prevents their execution by design. For businesses handling sensitive data, this layer of protection is essential, as it aligns with NIST SP 800-160 guidelines for system integrity.Beyond malware prevention, Secure Boot also enforces software authenticity, ensuring users aren’t tricked into running tampered versions of Windows or drivers. This is particularly relevant for enterprise deployments, where rogue firmware updates or supply-chain attacks (e.g., CCleaner malware) could compromise entire networks. The feature also simplifies compliance for standards like PCI DSS or HIPAA, as it provides an auditable mechanism for verifying system integrity.
> "Secure Boot isn’t just a security feature—it’s a foundational shift in how we trust our computers. Without it, the boot process is an unguarded gateway for attackers." — Mark Russinovich, Microsoft Technical Fellow
Major Advantages
- Malware Resistance: Blocks boot-sector viruses, rootkits, and firmware-based exploits by verifying all boot components.
- Software Integrity: Prevents tampered OS installations or unsigned drivers from executing.
- Compliance Alignment: Meets requirements for FIPS 140-2, NIST 800-160, and enterprise security frameworks.
- Hardware Protection: Reduces risk of BadUSB or Thunderspy attacks by securing the boot environment.
- Future-Proofing: Prepares systems for Windows 11 and UEFI 2.9+ features like Secure Boot for Containers.

Comparative Analysis
| Feature | Secure Boot (Enabled) vs. Legacy BIOS |
|---|---|
| Boot Process | Verifies digital signatures of all boot files (UEFI) vs. no verification (Legacy BIOS). |
| Malware Protection | Blocks bootkits and firmware exploits vs. vulnerable to MBR/boot-sector infections. |
| Driver Compatibility | Requires signed drivers (Windows 10+ compliant) vs. allows unsigned drivers. |
| Recovery Options | UEFI tools (e.g., `bcdedit`) for troubleshooting vs. limited to legacy boot managers. |
Future Trends and Innovations
The next iteration of Secure Boot will likely integrate with Trusted Platform Module (TPM) 2.0 to create a hardware-backed trust chain, where the TPM stores and protects Secure Boot keys. Microsoft’s Windows Defender System Guard already leverages this for memory integrity monitoring, and future updates may extend it to firmware integrity checks. Additionally, UEFI 2.9 (currently in development) introduces Secure Boot for Containers, allowing isolated environments to enforce signature verification independently of the host OS.For enterprises, automated Secure Boot enforcement via Microsoft Intune or Group Policy is on the horizon, reducing manual configuration errors. Meanwhile, open-source projects like Shim (used by Linux) continue to evolve, offering more flexibility for mixed-environment deployments. As firmware attacks grow more sophisticated, how to enable Secure Boot Windows 10 will no longer be a one-time setup—it will require ongoing key management and firmware updates to stay effective.
Conclusion
Enabling Secure Boot in Windows 10 is no longer optional—it’s a necessity for any system prioritizing security. The process is simple, but the implications are profound: a properly configured system is far less likely to fall victim to boot-level malware, firmware exploits, or supply-chain attacks. The trade-offs—such as compatibility with unsigned bootloaders—are outweighed by the reduced attack surface and compliance benefits. For IT administrators, the shift from Legacy BIOS to UEFI with Secure Boot is inevitable; the question is whether they’ll proactively enable it or react to a breach.The key takeaway is this: Secure Boot isn’t just about locking down Windows 10—it’s about securing the foundation of your entire system. By following the steps outlined here and staying informed on updates, you’re not just enabling a feature—you’re fortifying your digital infrastructure against threats that traditional antivirus tools can’t stop.
Comprehensive FAQs
Q: Can I enable Secure Boot on a Windows 10 system with Legacy BIOS?
A: No. Secure Boot requires UEFI firmware, not Legacy BIOS. If your system only offers Legacy mode, you’ll need to update the BIOS to UEFI mode (if supported) or use a UEFI-compatible motherboard. Some older systems may require a BIOS flash to enable UEFI.
Q: Will enabling Secure Boot break my dual-boot setup with Linux?
A: It depends. Most modern Linux distributions (e.g., Ubuntu, Fedora) include shim loaders that are signed by Microsoft, allowing them to boot under Secure Boot. However, older Linux kernels or custom bootloaders may fail. Solutions include:
Q: What should I do if Windows 10 fails to boot after enabling Secure Boot?
A: This usually indicates an unsigned driver or boot component. Troubleshoot with these steps:
1. Boot into Windows Recovery Environment (WinRE) via a USB drive.
2. Use `bcdedit` to check boot configuration:
```cmd
bcdedit /enum {bootmgr}
```
3. If a driver is unsigned, update it or exclude it via Group Policy (`gpedit.msc` > Computer Configuration > Administrative Templates > System > Driver Installation).
4. As a last resort, disable Secure Boot temporarily to identify the culprit.
Q: Does Secure Boot prevent all types of malware?
A: No. While it blocks boot-sector viruses and firmware-based malware, it doesn’t protect against:
Q: How do I check if Secure Boot is already enabled on my Windows 10 system?
A: Use one of these methods:
1. Via Command Prompt (Admin):
```cmd
bcdedit | find "secureboot"
```
```powershell
Get-FirmwareBootOption -BootOptionId 0 | Select-Object SecureBootEnabled
```
3. Via UEFI Setup: Restart, enter BIOS (usually Del/F2), and check the Security or Boot tab for Secure Boot status.
Q: Can I enable Secure Boot on Windows 10 Home edition?
A: Yes, but with limitations. Windows 10 Home supports Secure Boot natively, but Group Policy options (used to manage keys or exclusions) are only available in Pro/Enterprise. For Home users, rely on:
Q: What’s the difference between Secure Boot and BitLocker?
A: Secure Boot protects the boot process (preventing unauthorized code from loading), while BitLocker encrypts the disk (preventing unauthorized data access). Together, they form a defense-in-depth strategy:
Q: Will enabling Secure Boot void my warranty?
A: No, but modifying BIOS/UEFI settings improperly (e.g., flashing incorrect firmware) could. Most OEMs (Dell, HP, Lenovo) support Secure Boot by default, and Microsoft’s documentation confirms it doesn’t affect warranties. Always back up BIOS settings before making changes.
Q: How often should I update my Secure Boot keys?
A: Microsoft updates its Secure Boot keys periodically (typically annually). To stay current:
1. Check for UEFI firmware updates from your motherboard/OEM.
2. Use Windows Update (Settings > Update & Security > Advanced options > UEFI firmware settings).
3. For enterprises, automate key updates via WSUS or Intune policies.
Q: Can I disable Secure Boot later if needed?
A: Yes, but only if you have a valid reason (e.g., testing legacy software). To disable:
1. Restart and enter UEFI setup (usually F2/Del).
2. Navigate to Security or Boot tab.
3. Set Secure Boot to Disabled.
4. Save and exit. Note: This reduces security—re-enable it once testing is complete.
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of Viralcontentbee.