How to Safely Navigate Digital Leaks: Mitigating Cybersecurity Risks in a Data-Driven Era
The 2023 breach of a major cloud provider exposed 33 billion records—far surpassing the infamous Equifax incident. Yet, despite such high-profile failures, most organizations still treat digital leaks as an inevitability rather than a preventable risk. The reality is stark: 60% of cyber incidents stem from poor access controls or unpatched vulnerabilities, both of which fall under the broader challenge of leak navigating cybersecurity risks digital. The problem isn’t just technical—it’s cultural. Teams prioritize feature velocity over security audits, and executives often underestimate the cascading reputational damage a single exposed API key can trigger.
What separates resilient organizations from those left scrambling after a breach isn’t luck, but a disciplined approach to threat modeling. The difference between a minor data spill and a full-scale catastrophe often hinges on whether an incident was detected within hours or weeks. Yet, many security protocols remain reactive, focusing on firewalls and antivirus while neglecting the human and systemic factors that enable leaks. The truth is that leak navigating cybersecurity risks digital requires a multi-layered strategy—one that blends proactive monitoring, behavioral analytics, and a zero-trust mindset.
Consider the case of a mid-sized fintech firm that lost $12 million in a single weekend due to an unsecured developer environment. The attack vector? A misconfigured AWS bucket left exposed for six months. No sophisticated hacking was involved—just a fundamental failure to align development workflows with security best practices. This isn’t an outlier; it’s a pattern. The average cost of a data breach now exceeds $4.45 million, but the real cost—lost customer trust, regulatory fines, and operational paralysis—is often invisible until it’s too late. The question isn’t if a leak will occur, but how your organization will detect, contain, and recover from it before the damage spirals.

The Complete Overview of Leak Navigating Cybersecurity Risks Digital
The term leak navigating cybersecurity risks digital encompasses the strategies, tools, and cultural shifts needed to minimize data exposure across an organization’s digital footprint. It’s not solely about preventing breaches but about creating an adaptive security posture that evolves with emerging threats—from insider threats and third-party vulnerabilities to AI-driven attack vectors. The digital landscape has shifted from static perimeter defenses to a dynamic ecosystem where data flows across clouds, endpoints, and supply chains. Traditional security models, built on the assumption that threats originate from outside the network, are increasingly obsolete.
Modern leak navigating cybersecurity risks digital demands a paradigm shift: security must be embedded into every stage of the data lifecycle, from creation to deletion. This includes real-time monitoring of anomalous behavior (e.g., a user accessing files outside their role), automated patch management for zero-day exploits, and continuous red-team exercises to test resilience. The goal isn’t perfection—it’s reducing the attack surface to a point where leaks, when they occur, are contained before they escalate. Organizations that treat cybersecurity as a checkbox rather than a core competency are the ones that end up in headlines.
Historical Background and Evolution
The concept of digital leaks traces back to the early days of the internet, when universities and military networks first connected. The 1988 Morris Worm, one of the first major cyberattacks, exposed the fragility of unsecured systems. However, it wasn’t until the 2000s—with the rise of cloud computing and social media—that leaks became a mainstream concern. The 2013 Snowden revelations demonstrated how even highly classified systems could be compromised through insider access, while the 2017 Equifax breach (exposing 147 million records) proved that basic hygiene failures could have catastrophic consequences.
Table of Contents
- The Complete Overview of Leak Navigating Cybersecurity Risks Digital
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: What’s the most common cause of digital leaks?
- Q: How can small businesses implement leak navigation without breaking the budget?
- Q: Is encryption enough to prevent digital leaks?
- Q: How often should organizations test their leak detection capabilities?
- Q: What role does employee training play in leak navigation?
- Q: Can AI actually reduce false positives in threat detection?
Today, the evolution of leak navigating cybersecurity risks digital is being driven by three key factors: the proliferation of IoT devices (each a potential entry point), the rise of ransomware-as-a-service (lowering the barrier for amateur hackers), and the globalization of supply chains (where a single vendor’s lapse can expose an entire ecosystem). Regulatory frameworks like GDPR and CCPA have forced organizations to adopt stricter data handling practices, but compliance alone doesn’t equate to security. The most advanced threats—such as deepfake-driven phishing or quantum computing-enabled decryption—are still on the horizon, meaning the field of leak navigating cybersecurity risks digital is far from mature.
Core Mechanisms: How It Works
At its core, leak navigating cybersecurity risks digital relies on three interconnected mechanisms: prevention, detection, and response. Prevention involves hardening systems through encryption, access controls, and regular vulnerability assessments. Detection leverages tools like SIEM (Security Information and Event Management) and UEBA (User and Entity Behavior Analytics) to flag anomalies in real time. Response is where many organizations fail—having a playbook for isolating affected systems, communicating with stakeholders, and restoring operations without further exposure.
The most effective strategies integrate these mechanisms into a unified framework. For example, a zero-trust architecture assumes breach and verifies every access request, while deceptive technology (honey pots) lures attackers into traps to study their tactics. Meanwhile, automated incident response (AIR) systems can contain threats in minutes, reducing dwell time—the average time an attacker remains undetected, which currently sits at 21 days. The challenge lies in balancing these layers without creating friction that hinders productivity. The best practices in leak navigating cybersecurity risks digital recognize that security and usability aren’t mutually exclusive; they’re interdependent.
Key Benefits and Crucial Impact
Organizations that prioritize leak navigating cybersecurity risks digital gain more than just protection—they achieve operational efficiency, competitive advantage, and long-term sustainability. The financial stakes are clear: companies with mature security postures experience 30% lower breach costs and recover faster from incidents. Beyond dollars, the reputational impact is immeasurable. A single leak can erode decades of brand trust in weeks, as seen with companies like Facebook (Cambridge Analytica) and Uber (2016 breach cover-up). The intangible cost—lost innovation velocity, talent attrition, and investor confidence—often outweighs the direct financial hit.
Yet, the benefits extend to customers and partners as well. Consumers now demand transparency and accountability; 83% of respondents in a 2023 survey said they’d switch providers after a breach. For B2B relationships, a strong security posture can become a differentiator, especially in regulated industries like healthcare and finance. The organizations leading in leak navigating cybersecurity risks digital aren’t just surviving—they’re redefining what it means to be secure in a hyper-connected world.
— "Cybersecurity is no longer an IT problem; it’s a business problem. The companies that treat it as the latter will outperform those that treat it as the former."
— Gartner, 2023 Security & Risk Management Report
Major Advantages
- Reduced Financial Exposure: Proactive leak mitigation cuts breach costs by up to 40% through early detection and containment.
- Regulatory Compliance: Automated auditing and logging streamline adherence to GDPR, HIPAA, and other frameworks, avoiding fines.
- Enhanced Customer Trust: Transparent security practices improve brand loyalty and reduce churn post-incident.
- Operational Resilience: Zero-trust models and automated responses minimize downtime during attacks.
- Competitive Edge: Security becomes a value proposition, especially for enterprises targeting high-risk sectors like fintech or biotech.

Comparative Analysis
| Traditional Security Model | Modern Leak-Navigating Approach |
|---|---|
| Perimeter-focused (firewalls, VPNs) | Identity-centric (zero trust, MFA, continuous authentication) |
| Reactive (incident response after breach) | Proactive (predictive analytics, threat hunting) |
| Silos (IT and security operate independently) | Integrated (DevSecOps, security embedded in development) |
| Compliance-driven (checklist-based security) | Risk-driven (continuous assessment, adaptive controls) |
Future Trends and Innovations
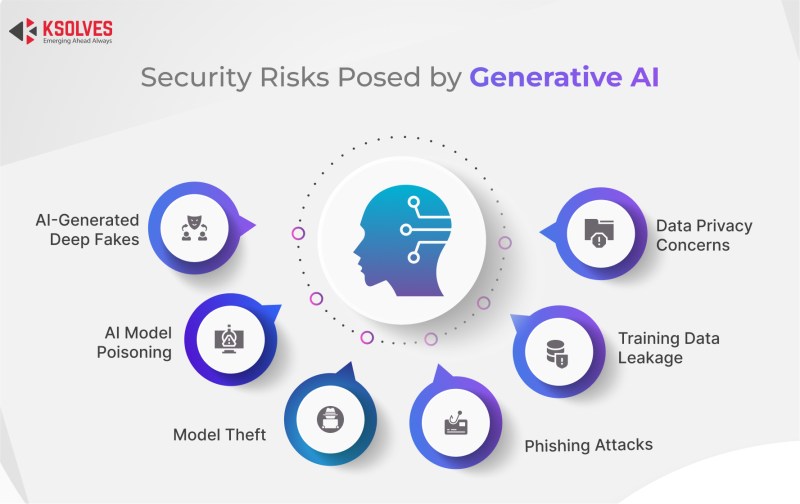
The next frontier in leak navigating cybersecurity risks digital will be shaped by AI, quantum computing, and the metaverse. AI-driven threat detection is already reducing false positives by 70%, but the real breakthrough will come from generative AI that can simulate attack scenarios in real time. Quantum-resistant encryption is on the horizon, forcing organizations to future-proof their cryptographic infrastructure. Meanwhile, the metaverse introduces new attack surfaces—virtual asset theft, deepfake-driven fraud, and supply-chain risks in digital marketplaces—demanding a rethink of traditional security paradigms.
Another critical shift will be toward human-centric security, where behavioral biometrics and contextual authentication replace passwords. The goal is to make security invisible to users while keeping it ironclad. Organizations that fail to adapt risk falling behind as threats evolve. The companies leading in leak navigating cybersecurity risks digital won’t just react to leaks—they’ll anticipate them, turning potential vulnerabilities into strategic advantages.
Conclusion
The landscape of leak navigating cybersecurity risks digital is no longer about building walls—it’s about building agility. The organizations that thrive in this era will be those that treat security as a dynamic, ever-evolving discipline rather than a static set of policies. The tools exist; the challenge is cultural. Leadership must champion security as a business enabler, not a cost center, and employees must be trained to recognize threats without stifling innovation.
Ignoring the risks of digital leaks is a luxury no organization can afford. The question is no longer if a breach will happen, but how prepared you’ll be when it does. The answer lies in a relentless focus on leak navigating cybersecurity risks digital—not as a destination, but as a continuous journey.
Comprehensive FAQs
Q: What’s the most common cause of digital leaks?
A: Misconfigured cloud storage (e.g., exposed S3 buckets) and phishing attacks account for over 50% of leaks. Insider threats—whether malicious or accidental—are also a major factor, particularly in industries handling sensitive data like healthcare or finance.
Q: How can small businesses implement leak navigation without breaking the budget?
A: Start with free tools like Google’s Security Command Center for cloud monitoring, enable multi-factor authentication (MFA) everywhere, and conduct quarterly phishing simulations. Partnering with managed security service providers (MSSPs) can also provide enterprise-grade protection at a fraction of the cost.
Q: Is encryption enough to prevent digital leaks?
A: No. While encryption protects data in transit and at rest, leaks often occur due to poor key management, unpatched systems, or social engineering. A layered approach—combining encryption, access controls, and behavioral analytics—is essential for comprehensive protection.
Q: How often should organizations test their leak detection capabilities?
A: Continuous red teaming and purple teaming (collaborative red/blue team exercises) are ideal, but at minimum, organizations should conduct quarterly penetration tests and annual third-party audits. The goal is to simulate real-world attack scenarios and refine response times.
Q: What role does employee training play in leak navigation?
A: Over 90% of breaches involve human error. Training should go beyond compliance modules—it must include simulated phishing campaigns, workshops on recognizing social engineering tactics, and clear incident reporting protocols. Culture matters: organizations where security is a shared responsibility see 60% fewer leaks.
Q: Can AI actually reduce false positives in threat detection?
A: Yes. AI and machine learning models analyze patterns across vast datasets to distinguish between legitimate activity and malicious behavior. Tools like Darktrace and CrowdStrike use AI to reduce false positives by up to 90%, allowing security teams to focus on high-risk alerts.
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of Viralcontentbee.