The Harsh Reality Check: Security Risks Protection You Can’t Afford to Ignore
The illusion of safety is the most dangerous myth in security. Whether you’re a corporate executive, a small business owner, or an individual navigating a hyper-connected world, the assumption that "it won’t happen to me" is a ticking time bomb. A reality check security risks protection exposes the cold truth: threats don’t discriminate. They exploit gaps—technical, human, or procedural—with surgical precision. The 2023 global cybercrime damage costs topped $8 trillion, yet 60% of breaches stem from avoidable oversights. Physical spaces aren’t immune either; from tailgating in office buildings to unsecured IoT devices in smart homes, vulnerabilities are everywhere. The question isn’t if you’ll face a security incident, but when—and how severely it will disrupt your life or operations.
What separates the resilient from the vulnerable isn’t luck, but a disciplined approach to security risks protection. It’s the difference between reacting to a breach and preventing one. Take the 2021 Colonial Pipeline ransomware attack: a single compromised password led to a national fuel crisis. Or the 2022 Uber breach, where an attacker accessed internal systems through a misconfigured cloud storage bucket. These aren’t isolated cases; they’re symptoms of a systemic failure to confront reality. The hard truth? Security isn’t a product you buy—it’s a mindset you cultivate. And that mindset starts with understanding the reality check security risks protection demands: awareness, adaptability, and action.
Yet most people and organizations operate under false security. They rely on outdated protocols, ignore warning signs, or assume compliance equals protection. The gap between perception and reality is where attackers thrive. A reality check security risks protection isn’t about fearmongering; it’s about equipping you with the knowledge to turn potential disasters into controlled risks. This article cuts through the noise to deliver a no-nonsense breakdown of the threats you face, how they manifest, and the concrete steps to neutralize them before they escalate.
The Complete Overview of Reality Check Security Risks Protection
The concept of reality check security risks protection isn’t about paranoia—it’s about operational hygiene. It’s the framework that forces you to ask: What are the most likely threats to my assets? How do they exploit human behavior, technical flaws, or procedural lapses? And what’s the cost of inaction? Unlike traditional security narratives that focus on tools (firewalls, encryption, CCTV), this approach prioritizes the people and processes that either fortify or fracture your defenses. For example, a reality check security risks protection might reveal that your employees’ password habits are your weakest link, or that your third-party vendors have lax security—both of which are far more critical than a single antivirus update.
This discipline demands a shift from reactive to proactive measures. Reactive security—like patching systems after a breach—is like locking the barn door after the horse has bolted. Proactive security risks protection, however, involves continuous threat modeling, employee training simulations, and real-time monitoring of anomalies. It’s about treating security as a dynamic ecosystem, not a static checklist. The stakes are higher than ever: a single misconfigured server can expose years of customer data, a phishing email can cripple a supply chain, and a physical security lapse can lead to theft or sabotage. The reality check isn’t just about identifying risks; it’s about quantifying their potential impact and prioritizing mitigation efforts accordingly.
Historical Background and Evolution
The origins of security risks protection trace back to military and intelligence strategies, where threat assessment was a matter of national survival. The Cold War era saw the rise of risk matrices and contingency planning, later adapted into corporate security frameworks. However, the digital revolution of the 1990s and 2000s forced a paradigm shift. Cybersecurity, once a niche concern, became a boardroom priority after high-profile incidents like the 2000 Love Bug virus, which infected 50 million computers. These early breaches exposed a critical flaw: security was reactive, not predictive. The reality check of the 2010s was that attackers had evolved into organized, profit-driven entities, using social engineering and zero-day exploits to bypass traditional defenses.
Table of Contents
- The Complete Overview of Reality Check Security Risks Protection
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: How often should I conduct a security risk assessment?
- Q: What’s the biggest misconception about security risks protection?
- Q: Can small businesses afford a reality check security risks protection framework?
- Q: How do I measure the effectiveness of my security risks protection strategy?
- Q: What’s the first step in implementing a reality check security risks protection plan?
Today, reality check security risks protection is a fusion of historical lessons and cutting-edge tactics. The 2017 WannaCry ransomware attack, which leveraged an NSA exploit, demonstrated how nation-state capabilities could weaponize vulnerabilities in civilian infrastructure. Meanwhile, the rise of insider threats—whether malicious or negligent—has forced organizations to adopt behavioral analytics and user entity behavior analytics (UEBA) to detect anomalies. The evolution isn’t just technological; it’s cultural. Modern security risks protection requires a holistic approach that integrates physical security, cybersecurity, and human factors. For instance, the 2020 Twitter Bitcoin scam wasn’t just a hack—it was a social engineering attack that exploited internal access controls and employee trust. The lesson? A reality check must account for the interplay between all three domains.
Core Mechanisms: How It Works
The mechanics of reality check security risks protection revolve around three pillars: threat intelligence, risk assessment, and continuous adaptation. Threat intelligence involves aggregating data from open-source feeds, dark web monitoring, and industry reports to anticipate attack vectors. Risk assessment, meanwhile, evaluates the likelihood and impact of each threat, assigning priorities based on business criticality. For example, a healthcare provider’s reality check would flag patient data breaches as high-risk due to regulatory fines and reputational damage, while a retail chain might prioritize payment card skimming at POS terminals. The final pillar—continuous adaptation—ensures that defenses evolve alongside emerging threats, such as AI-driven phishing or deepfake scams.
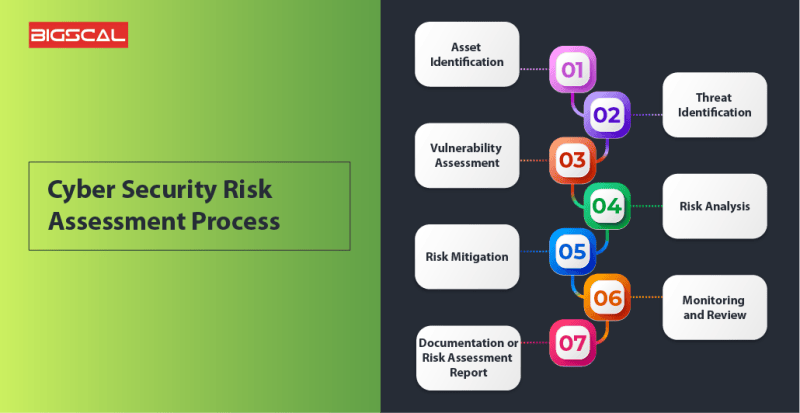
Implementation begins with a security risk assessment (SRA)**, which maps assets, identifies vulnerabilities, and simulates attack scenarios. Tools like penetration testing, red teaming, and vulnerability scanners provide empirical data, but the most critical input comes from human behavior analysis. A reality check security risks protection framework often includes tabletop exercises to test response protocols, phishing simulations to measure employee awareness, and third-party audits to uncover blind spots. For instance, a 2023 study found that 90% of breaches involved human error, yet only 20% of organizations conducted regular security awareness training. The mechanism isn’t just about technology; it’s about creating a culture where security is everyone’s responsibility. Without this human layer, even the most advanced protection measures can fail.
Key Benefits and Crucial Impact
The value of reality check security risks protection isn’t abstract—it’s measurable in dollars saved, downtime avoided, and reputational integrity preserved. Organizations that treat security as a continuous process rather than a compliance checkbox reduce breach costs by up to 70%, according to IBM’s 2023 Cost of a Data Breach Report. For individuals, the impact is equally tangible: a single identity theft incident costs an average of $1,200 to resolve, not to mention the stress and credit damage. The reality check isn’t just about preventing losses; it’s about maintaining trust. Customers, partners, and employees expect—and demand—protection in an era where data is the new currency. A breach isn’t just a financial hit; it’s a trust hit that can take years to recover.
Beyond financial and reputational safeguards, security risks protection enables resilience. Resilient systems don’t just survive attacks—they adapt and improve. For example, after the 2021 Kaseya ransomware attack, which disrupted 1,500 businesses, many organizations overhauled their backup and recovery strategies, leading to faster incident response times. The reality check here is that security isn’t a destination; it’s a journey. The most forward-thinking companies treat it as an ongoing investment, not a one-time expense. The question isn’t whether you’ll face a threat, but whether you’ll be ready when it arrives.
— "Security is not a product, but a process. The moment you think you’re secure, you’re already vulnerable."
— Bruce Schneier, Security Technologist
Major Advantages
- Proactive Threat Neutralization: By identifying and mitigating risks before they materialize, organizations avoid the cascading damage of a breach—financial, operational, and legal.
- Cost Efficiency: The average cost of a data breach in 2023 was $4.45 million. A reality check security risks protection framework reduces this by 40–60% through early detection and prevention.
- Regulatory Compliance: Frameworks like GDPR, HIPAA, and PCI DSS require rigorous risk assessments. A proactive approach ensures compliance while minimizing audit failures.
- Enhanced Decision-Making: Data-driven risk analysis allows leaders to allocate resources effectively, balancing security spend with business growth.
- Cultural Shift Toward Security: Regular training and simulations foster a security-conscious workforce, reducing human error—the root cause of 95% of breaches.

Comparative Analysis
| Traditional Security Approach | Reality Check Security Risks Protection |
|---|---|
| Reactive: Patches systems after a breach occurs. | Proactive: Identifies and mitigates threats before exploitation. |
| Tool-Centric: Relies on firewalls, antivirus, and encryption. | Human-Centric: Integrates behavioral analytics and employee training. |
| Static: Security policies are updated annually or after incidents. | Dynamic: Continuous monitoring and real-time adaptation. |
| Compliance-Driven: Meets minimum regulatory requirements. | Risk-Driven: Prioritizes threats based on business impact. |
Future Trends and Innovations
The next frontier of reality check security risks protection lies in artificial intelligence and predictive analytics. AI-driven threat detection can analyze millions of data points in real time, identifying patterns that human analysts might miss. For example, Darktrace’s AI flagged a zero-day ransomware attack at a UK healthcare provider by detecting unusual file encryption patterns—before any data was locked. Similarly, quantum-resistant encryption is becoming a priority as quantum computing threatens to obsolete current cryptographic standards. The future isn’t just about faster detection; it’s about anticipating threats before they emerge. Innovations like honeytoken technology (decoy data to lure attackers) and behavioral biometrics (authenticating users based on typing patterns) are pushing the boundaries of what’s possible.
However, the most significant shift will be in how organizations integrate security risks protection into their DNA. The traditional siloed approach—where cybersecurity, physical security, and HR operate independently—is obsolete. The future belongs to converged security, where these domains collaborate seamlessly. For instance, a smart building might use AI to detect tailgating in real time and automatically alert security, while a retail chain could cross-reference online fraud patterns with in-store transaction data. The reality check for tomorrow’s leaders is clear: security will no longer be an IT function; it will be a business function, embedded in every decision, from hiring to supply chain management.
Conclusion
The harsh truth is that reality check security risks protection isn’t optional—it’s a necessity in an era where threats are constant and evolving. The organizations and individuals who thrive are those who stop assuming security is someone else’s problem and take ownership of their vulnerabilities. This requires more than checklists or software; it demands a mindset that treats security as a competitive advantage. The cost of inaction isn’t just financial; it’s existential. A single oversight can erase years of progress, erode trust, and leave you exposed to exploitation. The good news? The tools and strategies to mitigate these risks are more accessible than ever. The bad news? Complacency is the only real threat.
Your next step isn’t to wait for a breach to happen—it’s to conduct your own reality check security risks protection today. Start by auditing your current defenses, training your team on emerging threats, and adopting a culture of continuous improvement. The future belongs to those who refuse to live under the illusion of safety. Will you be one of them?
Comprehensive FAQs
Q: How often should I conduct a security risk assessment?
A: A comprehensive assessment should be performed at least annually, with quarterly reviews of critical systems. However, if your organization undergoes major changes—such as mergers, new software deployments, or regulatory updates—conduct an assessment immediately. Continuous monitoring tools can also provide real-time risk scoring to flag anomalies between formal assessments.
Q: What’s the biggest misconception about security risks protection?
A: The biggest myth is that security risks protection is solely about technology. While tools like firewalls and encryption are essential, the majority of breaches stem from human error or misconfigured systems. A reality check reveals that the most robust defenses combine technical safeguards with employee training, vendor vetting, and proactive threat hunting.
Q: Can small businesses afford a reality check security risks protection framework?
A: Absolutely. Many small businesses assume they’re too small to be targeted, but 43% of cyberattacks aim at SMBs due to their perceived weaker defenses. A reality check security risks protection for small businesses starts with basic steps: multi-factor authentication, regular backups, employee cybersecurity training, and third-party risk assessments. Tools like free vulnerability scanners (e.g., Nessus, OpenVAS) and affordable MSSPs (Managed Security Service Providers) make professional-grade protection accessible without breaking the bank.
Q: How do I measure the effectiveness of my security risks protection strategy?
A: Effectiveness is measured through key performance indicators (KPIs) such as:
- Mean Time to Detect (MTTD) and Mean Time to Respond (MTTR) for incidents.
- Reduction in phishing susceptibility (tracked via simulated attacks).
- Compliance audit pass rates.
- Cost savings from avoided breaches.
- Employee participation in security training programs.
Q: What’s the first step in implementing a reality check security risks protection plan?
A: The first step is a threat and vulnerability assessment. This involves:
- Inventorying all assets (data, devices, applications, physical locations).
- Identifying potential threats (cyber, physical, insider, third-party).
- Evaluating vulnerabilities (misconfigurations, weak passwords, outdated software).
- Prioritizing risks based on likelihood and impact.
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of Viralcontentbee.