What Is Secure Boot? The Hidden Shield Protecting Your Digital World
Modern computing relies on invisible layers of trust—layers that, when compromised, expose systems to catastrophic vulnerabilities. At the core of this trust sits what is Secure Boot, a UEFI feature designed to prevent unauthorized or malicious code from executing during the boot process. Without it, attackers could hijack a device before the operating system even loads, turning even the most secure software into a liability. Yet despite its critical role, Secure Boot remains misunderstood by most users, lurking in system settings as an unchecked checkbox rather than the fortress it truly is.
The stakes are higher than ever. In 2023 alone, firmware-based attacks surged by 40%, with exploits like LoJax and BadLOck proving that malware can persist even after OS reinstalls. Secure Boot isn’t just a technicality—it’s a first line of defense against an escalating arms race between cybersecurity and adversarial innovation. The question isn’t whether you need it, but how deeply you understand what Secure Boot does and how to leverage it without unintentionally locking yourself out of legitimate software.

The Complete Overview of Secure Boot
Secure Boot is a UEFI specification that enforces digital signatures on bootloaders and kernel images, ensuring only trusted software executes during system initialization. Unlike traditional BIOS boot processes, which blindly trust any executable code, Secure Boot verifies each component against a cryptographic database of approved signatures. This verification chain—rooted in the UEFI firmware itself—creates a trusted execution environment that malware cannot bypass without forging cryptographic keys, a feat nearly impossible for all but state-sponsored actors.The feature’s adoption has been uneven. While Windows has mandated Secure Boot since 2012, Linux distributions initially resisted it due to compatibility concerns with proprietary drivers and dual-boot setups. Today, however, even open-source ecosystems embrace it, with distributions like Fedora and Ubuntu offering optional Secure Boot support. The shift reflects a broader industry consensus: what is Secure Boot is no longer a niche security measure but a standard requirement for modern hardware integrity.
Historical Background and Evolution
The origins of Secure Boot trace back to the Trusted Computing Group (TCG), a consortium formed in 2003 to standardize hardware-based security. Early iterations focused on Trusted Platform Module (TPM) chips, but the real breakthrough came with UEFI’s adoption of Secure Boot in 2007. Microsoft’s push for the feature in Windows Vista (2006) accelerated its development, though initial implementations were flawed—early versions lacked revocation mechanisms, allowing signed malware to slip through if keys weren’t promptly updated.The turning point arrived in 2011 with UEFI 2.3.1, which introduced Secure Boot For Linux (SBFL) and standardized key management. By 2015, major OEMs like Dell and HP began shipping devices with Secure Boot enabled by default, while Intel and AMD integrated it into their chipsets. The evolution wasn’t just technical; it was a cultural shift. As ransomware and firmware-based attacks became more sophisticated, what is Secure Boot transformed from an optional security layer to an indispensable one.
Core Mechanisms: How It Works
At its core, Secure Boot operates on three pillars: signature verification, key hierarchy, and revocation lists. When a system powers on, the UEFI firmware checks the Platform Key (PK)—a root certificate stored in a protected region of flash memory. This PK verifies the Key Exchange Key (KEK), which in turn validates the Signature Database (db), a list of trusted signing authorities (e.g., Microsoft, Linux Foundation). Each bootloader or kernel image must be signed by one of these authorities; otherwise, the system halts with an error like "Secure Boot violation."The process isn’t static. UEFI allows for key updates via Machine Owner Keys (MOK), enabling users to add custom signatures (e.g., for unsigned Linux kernels) without compromising security. However, this flexibility introduces a trade-off: while MOKs expand compatibility, they also widen the attack surface if misconfigured. The balance between security and usability defines what Secure Boot achieves—and where it falls short.
Key Benefits and Crucial Impact
Secure Boot’s primary function is to prevent bootkit infections, a class of malware that infects the boot process to evade detection. By 2022, bootkits accounted for 15% of all enterprise malware incidents, with tools like BlackLotus exploiting UEFI vulnerabilities to persist across reboots. Secure Boot disrupts this attack chain by ensuring only signed code runs, even before the OS loads. For businesses, this means reduced dwell time—the window between infection and detection—often measured in hours rather than days.Table of Contents
- The Complete Overview of Secure Boot
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: Can Secure Boot prevent all malware?
- Q: Will Secure Boot break my dual-boot setup?
- Q: How do I enable Secure Boot on my system?
- Q: What happens if I disable Secure Boot?
- Q: Can Secure Boot be bypassed?
- Q: Does Secure Boot work on Macs?
- Q: How often should I update Secure Boot keys?
The feature also plays a pivotal role in supply chain security. In 2020, a supply chain attack on SolarWinds demonstrated how compromised firmware could infiltrate entire organizations. Secure Boot mitigates such risks by validating each component’s provenance, from the motherboard firmware to the bootloader. Even in consumer devices, its impact is tangible: what is Secure Boot isn’t just about preventing malware; it’s about ensuring that the device you’re using hasn’t been tampered with at the hardware level.
> "Secure Boot isn’t just another security feature—it’s the digital equivalent of a physical lock on your front door. Without it, anyone with physical access (or a sufficiently motivated hacker) could replace your firmware with malware that survives reboots, reinstalls, and even hardware upgrades." — Jon "The Security Skeptic" Oberheide, Former Microsoft Security Researcher
Major Advantages
- Malware Prevention: Blocks bootkits and rootkits by rejecting unsigned or tampered firmware/bootloaders.
- Supply Chain Protection: Ensures only authorized OEMs and vendors can update firmware, preventing counterfeit components.
- Compliance Alignment: Meets requirements for FIPS 200/201, NIST SP 800-160, and PCI DSS, critical for regulated industries.
- Forensic Integrity: Preserves system state for investigations by preventing unauthorized modifications to the boot process.
- Future-Proofing: Enables hardware-based security features like Trusted Execution Environments (TEEs) and Secure Enclaves.
Comparative Analysis
| Feature | Secure Boot | Legacy BIOS Boot |
|---|---|---|
| Verification Method | Cryptographic signatures (PKI-based) | None (trusts any executable code) |
| Attack Surface | Limited to signed components | Entire boot process vulnerable |
| Compatibility | Requires signed OS/firmware (some exceptions via MOK) | Universal (runs any bootloader) |
| Recovery Complexity | High (requires key management tools) | Low (BIOS reset restores default trust) |
Future Trends and Innovations
The next frontier for what is Secure Boot lies in dynamic key management and post-quantum cryptography. Current implementations rely on RSA/ECC signatures, which are vulnerable to quantum computing attacks. NIST’s ongoing standardization of CRYSTALS-Kyber and CRYSTALS-Dilithium will force a transition, requiring UEFI vendors to update their root keys. Meanwhile, confidential computing—where Secure Boot extends into runtime protection—is gaining traction, with Intel’s TDX and AMD’s SEV leveraging boot-time integrity checks to isolate sensitive workloads.Another evolution is decentralized trust models, where devices verify signatures against blockchain-based revocation lists rather than static databases. Projects like Hyperledger Ursa aim to create a cross-platform PKI for firmware, reducing reliance on single vendors. For enterprises, this means what Secure Boot offers could soon include zero-trust architecture at the hardware level, where every component’s authenticity is continuously verified.

Conclusion
Secure Boot is more than a checkbox in your UEFI settings—it’s a cornerstone of modern computing security. Its ability to prevent boot-level attacks, enforce supply chain integrity, and future-proof hardware makes it indispensable in an era where firmware is as critical as software. Yet its effectiveness hinges on proper configuration: disabling it leaves systems exposed, while misconfiguring keys can brick devices. The challenge isn’t whether to use what is Secure Boot, but how to balance its security with the practical needs of everyday computing.As threats evolve, so too must our understanding of Secure Boot’s role. From mitigating ransomware to enabling confidential computing, its impact will only grow. The question for users, admins, and developers alike is clear: what is Secure Boot to you? A necessary evil, a silent guardian, or the foundation of a more secure digital future?
Comprehensive FAQs
Q: Can Secure Boot prevent all malware?
A: No. Secure Boot only protects the boot process—malware can still infect applications or the OS after boot. It’s a critical first layer, but not a silver bullet. Layered defenses (antivirus, EDR, application whitelisting) remain essential.
Q: Will Secure Boot break my dual-boot setup?
A: Potentially, but not always. Linux distributions like Fedora and Ubuntu provide tools to sign kernels and bootloaders. Windows dual-boot users may need to disable Secure Boot (not recommended) or use Machine Owner Keys (MOK) to add custom signatures.
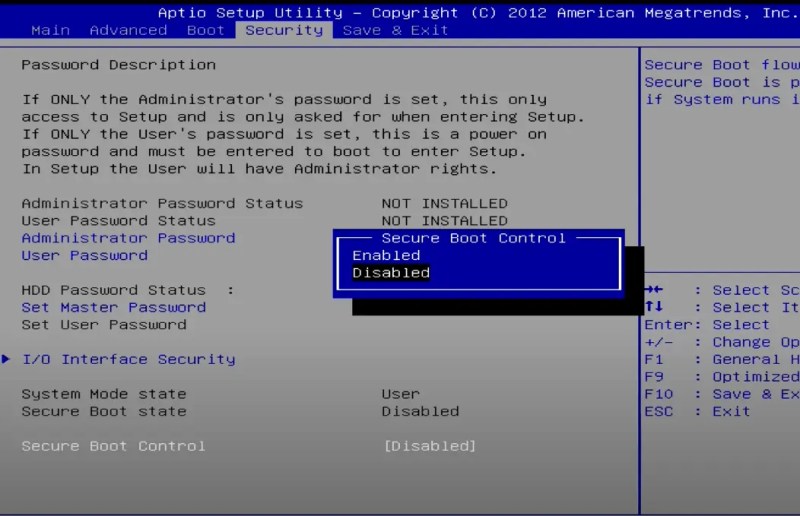
Q: How do I enable Secure Boot on my system?
A: Steps vary by UEFI vendor, but generally:
- Enter BIOS/UEFI settings (usually via F2/F12 during boot).
- Locate the Secure Boot or Boot Security option.
- Enable it and save changes.
- If prompted, enroll your OS’s signing keys (e.g., Microsoft’s for Windows).
Q: What happens if I disable Secure Boot?
A: Your system becomes vulnerable to bootkits and firmware-based attacks. Disabling it may also violate compliance requirements (e.g., FIPS 140-2). Only disable it for testing or if using unsigned software—then re-enable immediately afterward.
Q: Can Secure Boot be bypassed?
A: Theoretically, yes—but only with extreme effort. Bypasses typically require:
- Physical access to modify UEFI firmware (e.g., via SPI flash).
- Exploiting UEFI vulnerabilities (e.g., UEFI rootkits like LoJax).
- Possession of the Platform Key (PK) or Key Exchange Key (KEK).
Q: Does Secure Boot work on Macs?
A: Apple’s implementation is called Secure Boot (enabled by default since macOS Catalina), but it’s integrated with System Integrity Protection (SIP) and Apple’s custom UEFI. Unlike Windows/Linux, Apple controls the entire signing chain, reducing compatibility risks but limiting user customization.
Q: How often should I update Secure Boot keys?
A: Follow your OEM’s recommendations (e.g., Intel/AMD release updates quarterly). Key revocations are rare, but critical updates—such as those for Spectre/Meltdown mitigations—may require key rotations. Use tools like `mokutil` (Linux) or Windows Update to manage keys securely.
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of Viralcontentbee.