What Is a RSA? The Cryptographic Backbone Powering Digital Trust
When you type "what is a RSA" into a search engine, the results rarely scratch the surface of its true significance. RSA isn’t just an acronym—it’s the cryptographic foundation underpinning modern digital trust. From the HTTPS padlock in your browser to the blockchain securing your cryptocurrency, RSA’s mathematical elegance has quietly shaped the internet’s security infrastructure for decades. Yet despite its ubiquity, few understand how it transforms plaintext into unbreakable ciphertext—or why its vulnerabilities, when exploited, can unravel entire systems.
The question what is a RSA isn’t just about encryption; it’s about the balance between accessibility and security in an era where data breaches cost billions annually. RSA’s design—rooted in the computational difficulty of factoring large prime numbers—was revolutionary when introduced in 1977. Today, it remains the default choice for securing everything from government communications to e-commerce transactions, even as newer algorithms like ECC challenge its dominance. The tension between RSA’s historical reliability and emerging alternatives forces a critical examination: Is RSA still the gold standard, or is it time to rethink its role in cybersecurity?
At its core, RSA is more than a protocol—it’s a testament to how mathematics can outpace brute-force attacks. But its power comes with trade-offs: slower processing speeds, larger key sizes, and a reliance on prime-number generation that, if compromised, could expose entire networks. Understanding what is a RSA isn’t just academic; it’s essential for anyone navigating a digital landscape where encryption isn’t optional—it’s a necessity.

The Complete Overview of RSA Encryption
RSA encryption, when asked what is a RSA, refers to an asymmetric cryptographic algorithm that enables two parties to securely exchange messages without prior shared secrets. Unlike symmetric encryption (e.g., AES), which uses the same key for encryption and decryption, RSA leverages a pair of mathematically linked keys: a public key for encryption and a private key for decryption. This dual-key system solves the "key distribution problem," where securely sharing encryption keys was historically the weakest link in secure communications. The algorithm’s strength lies in its reliance on the integer factorization problem—the computational infeasibility of decomposing large semiprime numbers into their prime factors—making it resistant to eavesdropping even if the public key is widely disseminated.The practical implications of what is a RSA extend beyond theory. RSA’s adoption in SSL/TLS protocols (the backbone of HTTPS) ensures that credit card transactions, email communications, and VPN connections remain confidential. Its use in digital signatures verifies authenticity, preventing spoofing and ensuring non-repudiation—critical for legal and financial transactions. Even in post-quantum cryptography research, RSA serves as a benchmark, as quantum computers threaten to render its factorization-based security obsolete. The algorithm’s versatility has cemented its role as the de facto standard for secure key exchange, though its efficiency trade-offs (e.g., slower encryption/decryption compared to symmetric methods) necessitate hybrid approaches in modern systems.
Historical Background and Evolution
The origins of what is a RSA trace back to 1977, when Ron Rivest, Adi Shamir, and Leonard Adleman—mathematicians at MIT—published their groundbreaking paper introducing the algorithm. Though the concept of public-key cryptography predates their work (Whitfield Diffie and Martin Hellman’s 1976 paper on Diffie-Hellman key exchange laid early groundwork), RSA was the first practical implementation. The trio’s breakthrough hinged on two mathematical insights: modular arithmetic and the trapdoor function—a function easy to compute in one direction (e.g., multiplying primes) but nearly impossible to reverse (factoring the product). Their choice of prime numbers as the foundation was strategic; at the time, no efficient factoring algorithm existed for numbers with hundreds of digits.RSA’s adoption was initially slow due to export restrictions on cryptographic technology (the U.S. government classified it as a munition until 2000). However, the algorithm’s resilience in the face of early attacks—such as the 1994 factorization of RSA-129 (a 129-digit number cracked via distributed computing)—proved its robustness. The 1990s marked RSA’s commercialization, with RSA Security (founded by Rivest, Shamir, and others) licensing the technology to corporations and governments. By the 2000s, what is a RSA became synonymous with online security, as browsers integrated it into HTTPS, and organizations like PKI (Public Key Infrastructure) standardized its use. Today, RSA keys of 2048 bits are considered secure against classical computing attacks, though 3072-bit or 4096-bit keys are recommended for long-term protection.
Core Mechanisms: How It Works
To grasp what is a RSA at a functional level, one must dissect its three-phase process: key generation, encryption, and decryption. Key generation begins with selecting two large prime numbers, p and q, each typically 1024+ bits in length. These primes are multiplied to form the modulus (n = p × q), a semiprime number that defines the key pair’s strength. The public exponent (e) is chosen as a small odd number (commonly 65537) that is coprime with (p-1)(q-1). The private exponent (d) is derived using modular multiplicative inverse calculations: d ≡ e⁻¹ mod (p-1)(q-1). The public key (e, n) is shared openly, while the private key (d, n) is kept secret.Table of Contents
- The Complete Overview of RSA Encryption
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: What is a RSA in simple terms?
- Q: How does RSA encryption work step-by-step?
- Q: Is RSA still secure in 2024?
- Q: What are the main differences between RSA and ECC?
- Q: Can RSA be used for digital signatures?
- Q: What are the biggest threats to RSA security?
- Q: How does RSA relate to HTTPS and SSL/TLS?
- Q: Are there any real-world examples of RSA failures?
- Q: What is the future of RSA in post-quantum cryptography?
Encryption transforms plaintext into ciphertext using the public key via modular exponentiation: C ≡ Mᵉ mod n, where M is the plaintext message. Decryption reverses this with the private key: M ≡ Cᵈ mod n. The security relies on the fact that, without p and q, computing d from e and n is computationally infeasible for large numbers. For example, a 2048-bit RSA key has a modulus with ~600 decimal digits—factorizing it would require 10⁸⁰+ operations on a classical computer, making brute-force attacks impractical. However, quantum computers using Shor’s algorithm could theoretically break RSA by efficiently factoring large numbers, underscoring the need for post-quantum alternatives.
Key Benefits and Crucial Impact
The question what is a RSA reveals an algorithm that has redefined secure communication by solving problems that symmetric encryption could not. Its asymmetric nature eliminates the need for a pre-shared secret, addressing the key distribution problem that plagued early cryptographic systems. This innovation enabled secure key exchange protocols like Diffie-Hellman, which RSA later enhanced by providing authentication via digital signatures. In an era where data breaches expose millions of records annually, RSA’s ability to encrypt data without prior coordination has become indispensable. Governments, financial institutions, and tech giants rely on it to protect sensitive information, from classified military communications to patient health records under HIPAA.RSA’s impact extends beyond security into trust infrastructure. Digital signatures, a direct application of RSA, verify the integrity and authenticity of documents, code, and transactions. When a user signs a contract with an RSA-encrypted signature, the recipient can confirm it was created by the private key corresponding to the sender’s public key—preventing forgery. This mechanism underpins blockchain technology, where RSA-like signatures (though often replaced by ECDSA for efficiency) ensure the immutability of ledgers. Even passwords stored in databases are often hashed using RSA-based key derivation functions, adding an extra layer of protection against rainbow table attacks.
> "RSA didn’t just secure the internet—it made the internet possible. Without it, the web would be a lawless frontier where every transaction could be intercepted or altered." — Bruce Schneier, Cryptographer and Security Expert
Major Advantages
Understanding what is a RSA highlights five critical advantages that have solidified its dominance:- Asymmetric Security: Eliminates the need for a shared secret, solving the key distribution dilemma inherent in symmetric encryption.
- Non-Repudiation: Digital signatures created with RSA private keys cannot be denied, providing legal and financial accountability.
- Scalability: Public keys can be freely distributed, enabling secure communication between parties with no prior relationship.
- Versatility: Used in encryption, decryption, and key exchange, RSA supports a wide range of cryptographic protocols (e.g., TLS, PGP, SSH).
- Proven Track Record: Decades of real-world use with no major breaches (when implemented correctly) have earned it industry trust.

Comparative Analysis
While what is a RSA dominates discussions on encryption, alternatives like Elliptic Curve Cryptography (ECC) and Diffie-Hellman (DH) offer trade-offs in speed and key size. Below is a comparative breakdown:| Feature | RSA | ECC |
|---|---|---|
| Key Size | 2048-bit ≈ 112-bit security | 256-bit ≈ 112-bit security |
| Speed | Slower (modular exponentiation) | Faster (elliptic curve operations) |
Quantum Resistance
| Vulnerable to Shor’s algorithm |
Vulnerable to Shor’s algorithm |
|
| Use Cases | Digital signatures, TLS, PKI | Mobile security, IoT, modern TLS |
Future Trends and Innovations
The question what is a RSA today is increasingly paired with inquiries about its longevity. While RSA remains unchallenged in classical computing, the rise of quantum computing forces a reckoning. NIST’s post-quantum cryptography standardization project has identified RSA as vulnerable to Shor’s algorithm, which can factor large numbers exponentially faster than classical methods. This has spurred interest in hybrid cryptographic systems, combining RSA with post-quantum algorithms (e.g., CRYSTALS-Kyber) to future-proof security. Meanwhile, homomorphic encryption—allowing computations on encrypted data without decryption—may reduce RSA’s dominance in cloud computing, where data processing occurs on third-party servers.Another evolution is zero-trust architectures, where RSA’s role in identity verification (via certificates) is being supplemented by passwordless authentication and biometric keys. As organizations adopt YubiKey or Windows Hello, the traditional RSA-based PKI may face disruption. Yet, RSA’s legacy persists in blockchain, where its signature schemes remain foundational despite the shift toward ECDSA for efficiency. The future of what is a RSA hinges on its ability to adapt—whether through hybrid models, quantum-resistant variants, or entirely new cryptographic paradigms.
Conclusion
RSA’s story is one of resilience and adaptability. From its inception as a theoretical breakthrough to its current status as the bedrock of digital trust, what is a RSA encapsulates the intersection of mathematics and real-world security needs. Its ability to secure communications without pre-shared secrets was revolutionary, and its enduring relevance—despite newer algorithms—speaks to its foundational importance. Yet, the looming threat of quantum computing serves as a reminder that no cryptographic system is eternal. The transition to post-quantum solutions will redefine what is a RSA in the coming decades, but its principles will likely influence the next generation of encryption.For individuals and organizations alike, understanding RSA isn’t just about grasping an algorithm—it’s about recognizing the invisible infrastructure that protects modern life. Whether you’re encrypting an email, verifying a software update, or conducting a financial transaction, RSA is the silent guardian ensuring those actions remain secure. As cryptography evolves, RSA’s legacy will be measured not just by its past achievements, but by its ability to inspire the next wave of secure communication.
Comprehensive FAQs
Q: What is a RSA in simple terms?
A: RSA is a public-key encryption method that uses two keys: one public (for encryption) and one private (for decryption). It allows secure data exchange without pre-sharing secrets, forming the basis of HTTPS, digital signatures, and secure communications.
Q: How does RSA encryption work step-by-step?
A: RSA operates in three steps:
- Key Generation: Two large primes (p, q) are multiplied to create a modulus (n), and public/private exponents (e, d) are calculated.
- Encryption: Plaintext is encrypted using the public key via modular exponentiation (C ≡ Mᵉ mod n).
- Decryption: Ciphertext is decrypted with the private key (M ≡ Cᵈ mod n).
Q: Is RSA still secure in 2024?
A: RSA remains secure against classical computing attacks when using 2048-bit or larger keys. However, it is vulnerable to quantum computers using Shor’s algorithm, which can factor large numbers efficiently. Organizations are transitioning to post-quantum cryptography or hybrid systems (e.g., RSA + Kyber) to mitigate this risk.
Q: What are the main differences between RSA and ECC?
A: The primary differences are:
- Key Size: RSA requires larger keys (e.g., 2048-bit) for equivalent security compared to ECC (e.g., 256-bit).
- Speed: ECC is faster and more efficient, especially on mobile/embedded devices.
- Quantum Resistance: Both are vulnerable to quantum attacks, but ECC may be slightly more efficient in hybrid post-quantum setups.
- Use Cases: RSA dominates in legacy systems (PKI, TLS), while ECC is preferred for modern applications (IoT, blockchain).
Q: Can RSA be used for digital signatures?
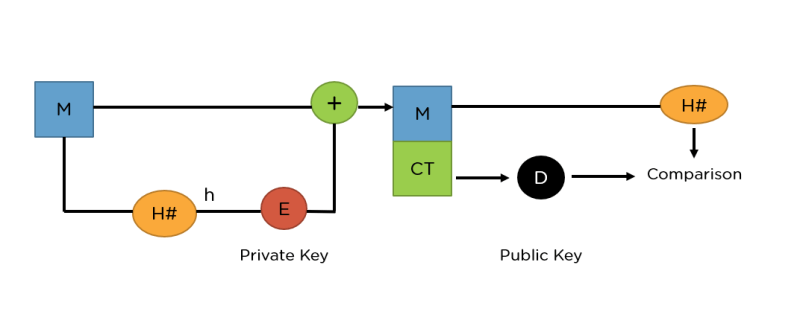
A: Yes. RSA is widely used for digital signatures, where the sender’s private key signs a hash of the message, and the recipient’s public key verifies it. This ensures authenticity, integrity, and non-repudiation, making it essential for contracts, software updates, and blockchain transactions.
Q: What are the biggest threats to RSA security?
A: The primary threats to RSA include:
- Quantum Computing: Shor’s algorithm can break RSA by factoring large numbers.
- Side-Channel Attacks: Timing or power analysis can leak private key information.
- Weak Key Generation: Poorly chosen primes or small key sizes reduce security.
- Implementation Flaws: Bugs in software (e.g., Heartbleed) can expose private keys.
- Social Engineering: Compromising private keys via phishing or insider threats.
Q: How does RSA relate to HTTPS and SSL/TLS?
A: RSA is a core component of SSL/TLS protocols, which secure HTTPS connections. During the TLS handshake, RSA can:
- Authenticate the server (via its RSA certificate).
- Exchange symmetric keys (e.g., AES) for session encryption.
- Enable RSA key exchange (though ECDHE is now more common for forward secrecy).
Q: Are there any real-world examples of RSA failures?
A: Yes, though rare, RSA-related breaches often stem from implementation errors rather than the algorithm itself. Notable cases include:
- DigiNotar (2011): A Dutch CA’s private key was compromised, leading to fraudulent SSL certificates for Google and other sites.
- RSA SecurID (2011): A flaw in RSA’s token-based authentication was exploited to bypass two-factor security.
- Heartbleed (2014): While primarily an OpenSSL bug, it exposed private keys in memory, affecting RSA-based systems.
Q: What is the future of RSA in post-quantum cryptography?
A: RSA’s future hinges on hybrid systems and quantum-resistant variants. NIST’s post-quantum standardization process may lead to:
- Hybrid Schemes: Combining RSA with lattice-based or hash-based algorithms (e.g., RSA + CRYSTALS-Kyber).
- Larger Key Sizes: Using 4096-bit or 8192-bit RSA as a stopgap until quantum-safe replacements are standardized.
- Phase-Out in Favor of PQC: Long-term, RSA may be replaced entirely by NIST-approved post-quantum algorithms (e.g., Dilithium for signatures).
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of Viralcontentbee.